
Published: |Last updated:
Listen to this article
Show Quick ReadConcise summary from this article
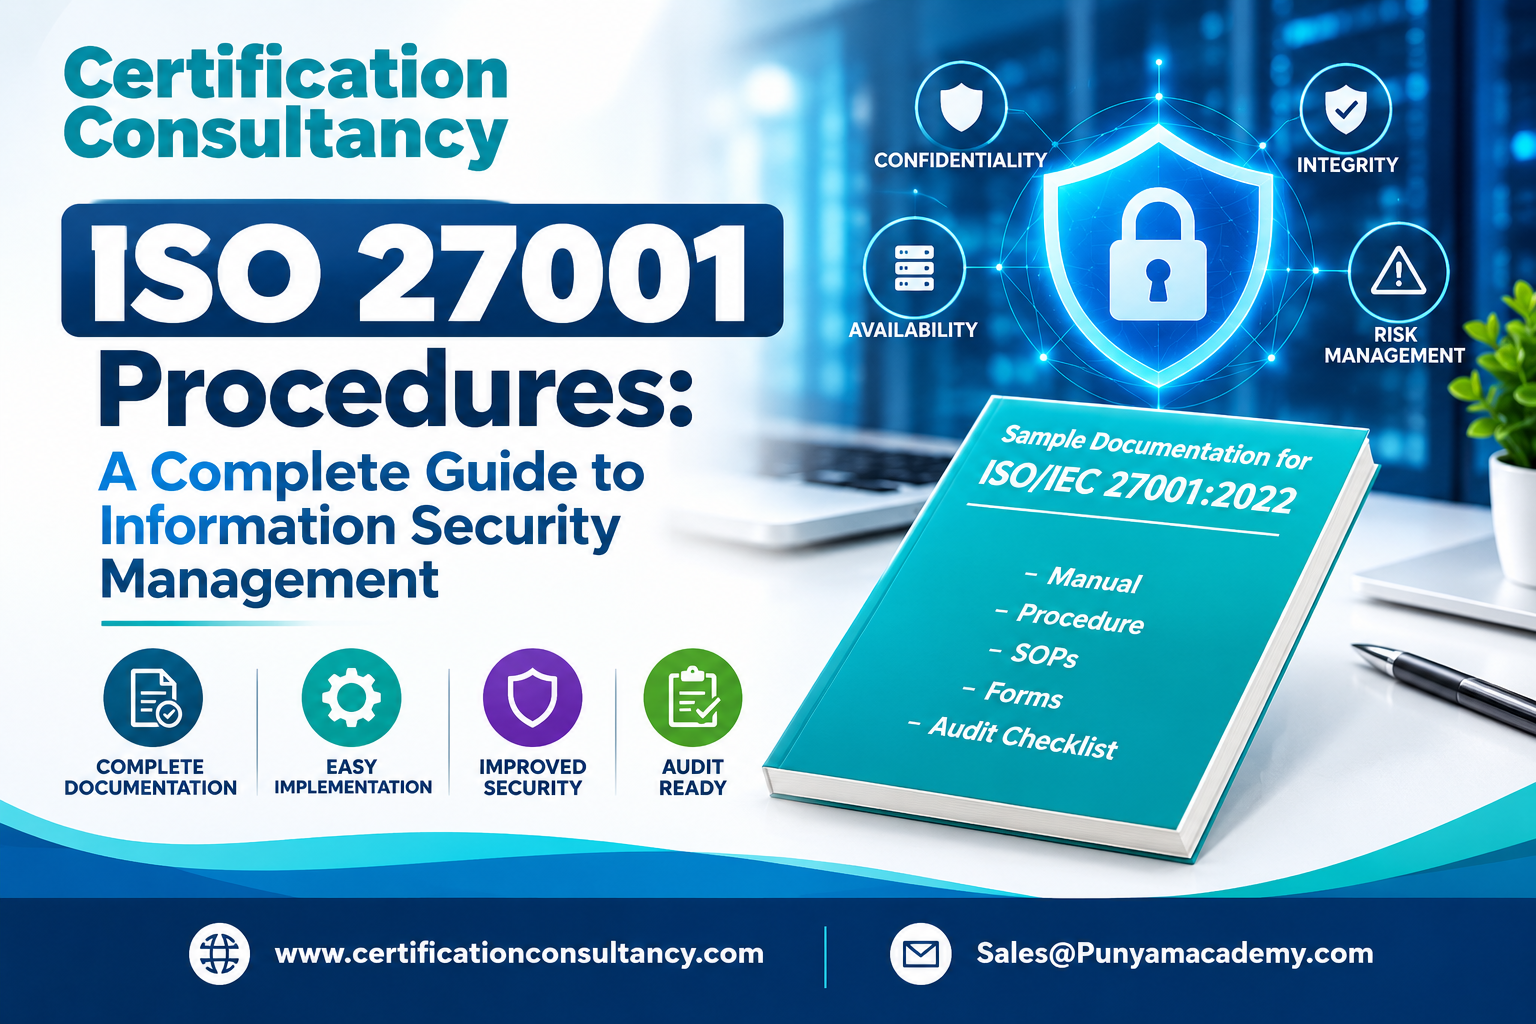
Information security has emerged as a significant aspect of current corporate processes. Companies process customer data, financial information, intellectual property, personnel data, and various other kinds of sensitive information on a regular basis. ISO 27001 procedures assist organizations in creating a systematic framework for information security risk management and development of ISMS (Information Security Management System). ISO/IEC 27001:2022 sets out requirements related to the establishment, implementation, maintenance, and continuous improvement…
Ask AI About This Article
Answers are limited to information in this article.
Information security has emerged as a significant aspect of current corporate processes. Companies process customer data, financial information, intellectual property, personnel data, and various other kinds of sensitive information on a regular basis. ISO 27001 procedures assist organizations in creating a systematic framework for information security risk management and development of ISMS (Information Security Management System).
ISO/IEC 27001:2022 sets out requirements related to the establishment, implementation, maintenance, and continuous improvement of ISMS.
What Are ISO 27001 Procedures?
ISO 27001 procedures are written documents that describe how certain information security tasks and procedures are carried out and controlled. These procedures assist employees in understanding their roles in relation to their duties and responsibilities in carrying out the process.
Procedures depend on the scope and risks of the organisation and could include procedures for access control, information security incident management, asset management, backup, risk management, supplier security, business continuity, and other information security tasks.
Clearly defined procedures can enhance the management of the ISMS because these relate the information security requiremsents to the organisational processes.
Importance of ISO 27001 Procedures
A good procedure ensures a practical basis for putting into effect the measures that govern information security. Rather than depending solely on policy statements, an organization can develop procedures for carrying out necessary tasks and creating proper documentation.
ISO 27001 encourages the use of a risk-based model that makes it easier for organizations to understand and mitigate their information security risks based on their particular situation.
Clear procedures can help organizations:
- Define responsibilities for information security activities
- Establish consistent methods for managing security processes
- Support risk assessment and risk treatment activities
- Improve control over sensitive information
- Maintain evidence of completed activities
- Support internal audits and management reviews
- Encourage continual improvement of the ISMS
Key Areas Covered by ISO 27001 Procedures
These will depend on the organizational circumstances, threats, processes, and ISMS scope. Some of the typical areas could be ISRM, access management, incident handling, asset management, document control, backup management, supplier relationships, and business continuity planning.
Procedures should be realistic and appropriate for the organization, not just developed for the sake of producing more documentation. These should specify the person doing the task, what has to be done, by what time, and what records need to be kept.
Role of an ISO 27001 Manual
An ISO 27001 manual would give a framework that will help an organization comprehend the structure of its ISMS. Where procedures describe particular actions, the manual could compile some necessary information concerning the ISMS, such as its scope, policies, organizational responsibilities, processes, and information security approach.
The manual and the procedure should complement each other, the former providing a framework and the latter describing how to implement particular processes.
ISO 27001 Documents and Procedures
ISMS documents assist in the proper planning, implementation, operation, monitoring, and improvement of an ISMS. The document structure may consist of policies, procedures, risk information, records, plans, registers, and any other type of documentation needed for the organization’s security.
The main idea of the ISO/IEC 27001 standard is the management of information security by way of a systematic approach aimed at ensuring the confidentiality, integrity, and availability of information.
Documentation should also be controlled. It is important to make sure that documents are always current, available to authorized users, properly reviewed, and updated. In this way, employees have access to the right information, and the organization shows how its ISMS works.
How to Develop Effective Procedures
When developing ISO 27001 procedures, organizations should first understand their information security risks and operational requirements. Each procedure should then be written in clear language and assigned to the appropriate responsible personnel.
A practical procedure generally includes its purpose, scope, responsibilities, process steps, related controls or requirements, and records to be maintained. Procedures should also be reviewed periodically to ensure they remain suitable when business processes, technology, risks, or organizational requirements change.
ISO/IEC 27001 is designed around continual improvement, so procedures should not be treated as static documents. They should evolve as the organization learns from incidents, audits, risk assessments, and changes in its operating environment.
Conclusion
Structured ISO 27001 procedures offer a solution for consistent handling of information security processes within organizations. In combination with adequate documentation, clearly assigned roles, risk assessment, and improvements, such procedures can enhance the whole ISMS and improve its performance in the field of information security management.
Certification Consultancy offers structured ISO 27001 documents and consultancy services for organizing the ISMS structure according to your information security needs.
Promote your articles nowCheck for details
Choose a promotion package
Choose a package below, scan the QR code and pay the displayed amount for 20 days.
After payment, email your article title and payment screenshot to info@yourneeds.asia. Once confirmation is received, one of our administrators will activate the promotion.
Choose where your promoted article receives extra visibility
Promotion changes presentation and placement for the selected period. It does not guarantee traffic, enquiries, search ranking or sales.
Priority visibility in the VIP Lounge, promoted shelves and highlighted article areas.
Top-style highlighting in article directories, homepage feeds and promoted article blocks.
Premium styling across supported article feeds, recommendations and directory placements.
Featured presentation in supported homepage, category, directory and related-article areas.
Build a stronger online presence for your business
Get Your Website for ₹15,000
Are you listed and don't have a website for your business? We can plan, design and launch a responsive website that makes your business easier to understand and contact.
Get My WebsiteSEO Starts from ₹10,000/Month
Improve how your business is presented across Google, local listings and AI-powered search results with ongoing SEO, content and authority-building work.
Improve My VisibilitySuggested Articles
View all articles
Best Workday HCM Training in Bangalore at TechMyIndia
Technology has transformed the way enterprises work with their employees. Information pertaining to workforce plus organizational plus human resource (HR) activities and processes…
Best ServiceNow ITAM Training In Hyderabad At TechMyIndia To Master Practical IT Asset Management
Technology professionals today manage more than just computers and software. A company may have laptops, servers, applications, licenses, cloud resources and many other technology…
Best Workday Finance Training in Bangalore at TechMyIndia: Learn Finance Technology the Practical Way
Finance is no longer limited to using Excel sheets and reports. Organizations use technology to manage financial information, business processes and reporting. As a…
Best Workday HCM Training In Noida at TechMyIndia: A Pragmatic Approach to Learning Workday HCM
Human resources technology is witnessing rapid changes, and the demand for professionals who understand HR processes and enterprise platforms is growing. Workday HCM has…
Latest Blog Posts
View all articles
New Flats in Pune City Guide | Real Estate Talk
Explore the New Flats in Pune City Guide 2026 from Real Estate Talk. Discover current residential developments, apartment configurations, pricing trends, amenities, connectivity, and…
LMPC Registration in India: Certificate Requirements for Importers, Packers and Manufacturers Under Rule 27
Every business that imports, packs or manufactures pre-packaged goods for sale in India must comply with the Legal Metrology law. The central requirement is…
How to Choose a Reliable Frozen Sweet Potato Fries Supplier?
Choosing the right frozen sweet potato fries supplier is an important decision for distributors, retailers, and foodservice businesses. A reliable supplier should provide consistent…
Ultimate Guide to Buying Frozen Sweet Potato Fries for Foodservice
Introduction Sourcing high-quality frozen sweet potato fries is an important part of successful foodservice operations. Restaurants, foodservice buyers, distributors, and brand managers need to…
From Madhapur Search to AI Discovery Best SEO Company Madhapur Done it right 2026
From Madhapur Search to AI Discovery: How YourNeeds.asia Builds a 360° SEO Visibility Engine for Local Businesses A customer looking for a business in…
BBQ Catering in Karachi: Delicious Grilled Food for Every Occasion
When it comes to outdoor gatherings and celebrations, BBQ is one of the most popular food choices. From family get-togethers and birthday parties to…