
Published: |Last updated:
Listen to this article
Show Quick ReadConcise summary from this article
Introduction Information security is one of the critical components in the operation of any modern organization. Organizations utilize various computing devices, cloud services, networks, and software applications to keep their critical information secure. Failure to implement adequate measures will result in security risks, such as unauthorized access, cyber-attacks, data loss, or other information breaches. An efficient Information Security Management System (ISMS) assists organizations in the identification and management of security…
Ask AI About This Article
Answers are limited to information in this article.
Introduction
Information security is one of the critical components in the operation of any modern organization. Organizations utilize various computing devices, cloud services, networks, and software applications to keep their critical information secure. Failure to implement adequate measures will result in security risks, such as unauthorized access, cyber-attacks, data loss, or other information breaches. An efficient Information Security Management System (ISMS) assists organizations in the identification and management of security risks.
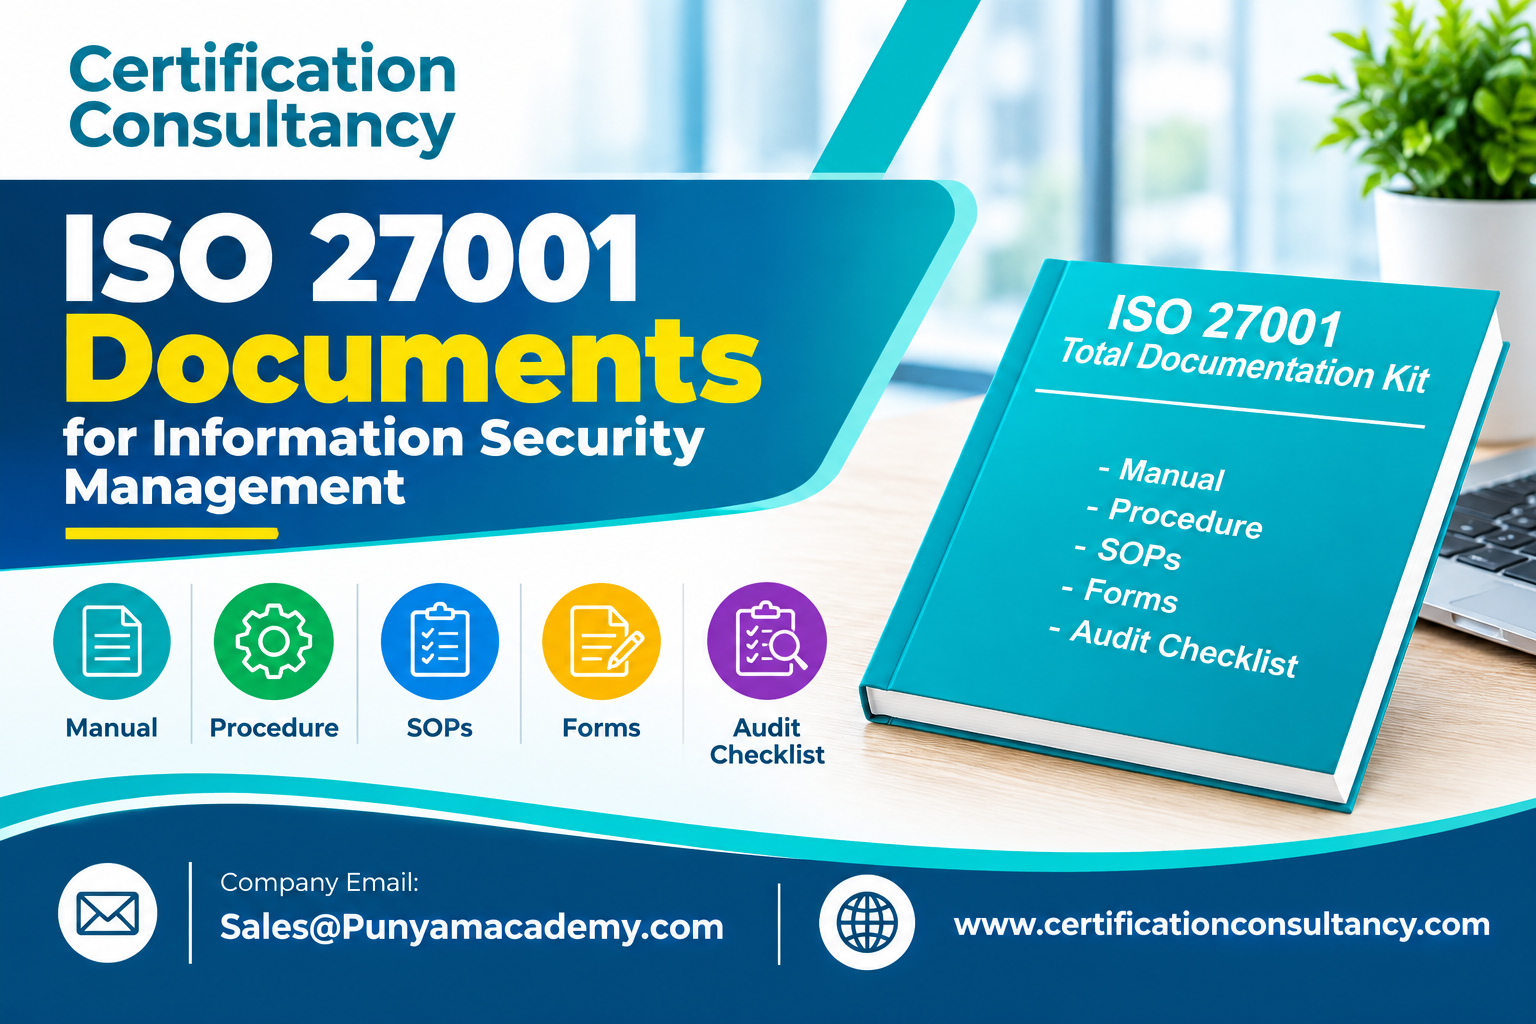
ISO 27001 Documents aid organizations in the implementation and management of ISMS in compliance with ISO/IEC 27001 standards.
What Are ISO 27001 Documents?
The ISO 27001 documents refer to manuals, policies, procedures, forms, and records that facilitate the operation of the information security management system. Such documents give explanations on planning, implementation, monitoring, and improvement of security processes.
Documentation helps businesses develop a standardized way of securing information. It also gives employees clear directions concerning their duties and controls they have to undertake.
A good documentation framework can assist firms in industries including IT services, software development, business process outsourcing, consulting, and many more.
Why Is ISO 27001 Documentation Important?
Documentation helps turn information security requirements into practical business activities. Without clear instructions and records, organizations may find it difficult to apply security controls consistently.
The main benefits include:
- Better risk management: Documents help organizations identify information security risks and plan suitable controls.
- Clear responsibilities: Policies and procedures explain who is responsible for specific security activities.
- Consistent processes: Documented methods help employees follow established information security practices.
- Audit preparation: Records and checklists help organizations review their ISMS and identify areas for improvement.
- Continual improvement: Audit findings, corrective actions, and management reviews help strengthen the system over time.
Documentation should reflect the organization’s actual activities, risks, and applicable requirements rather than simply being prepared for an audit.
Key Documents Required for an ISO 27001 Management System
An effective ISMS uses different types of documents to support planning, implementation, operation, and evaluation.
- ISO 27001 Manual
The ISO 27001 Manual provides an overview of the organization’s information security management system. It describes the ISMS scope, organizational responsibilities, key processes, and the approach used to address applicable standard requirements.
It acts as a central reference for understanding how the information security system operates. Organizations should customize the manual to reflect their business activities, locations, processes, and security needs.
- Information Security Policies
Policies establish the organization’s direction and expectations for protecting information. Depending on the organization’s needs, these may cover access control, passwords, acceptable use, backup, data protection, incident reporting, remote working, and other security topics.
Policies should be communicated to relevant employees and reviewed when business activities or security risks change.
- Procedures and Standard Operating Procedures
Procedures explain how specific ISMS activities are carried out. They may cover document control, internal audits, corrective actions, incident management, access management, and other relevant processes.
Standard operating procedures provide more detailed instructions for routine tasks. Together, these documents help employees understand how to apply security controls in daily operations.
- Forms, Templates, and Records
Forms and templates help organizations record information in a consistent format. Examples include risk assessment records, incident reports, training records, access reviews, corrective action reports, and management review records.
Maintaining accurate records helps demonstrate that planned activities are being performed and reviewed.
- Risk Assessment and Statement of Applicability
Risk assessment is a key part of information security management. Organizations identify relevant risks, evaluate their potential impact, and determine appropriate treatment actions.
The Statement of Applicability records the security controls selected or excluded, with appropriate justification. These documents should be consistent with the organization’s risk assessment and treatment decisions.
- Internal Audit Checklist
An internal audit checklist helps auditors review whether the ISMS processes are implemented and operating as intended. It can cover relevant requirements, policies, procedures, risk controls, and supporting records.
Audit findings should be documented, investigated, and addressed through appropriate corrective actions.
How to Prepare ISO 27001 Documents
Organizations can follow a practical sequence when preparing their documentation:
- Define the ISMS scope: Identify the services, locations, departments, and information assets covered by the system.
- Understand the requirements: Review ISO/IEC 27001 and determine which requirements apply to the organization.
- Assess information security risks: Identify relevant threats, vulnerabilities, and potential business impacts.
- Prepare the documents: Develop the manual, policies, procedures, risk records, and supporting templates needed for the system.
- Implement the documented processes: Assign responsibilities and communicate requirements to employees.
- Conduct internal audits: Review implementation, identify gaps, and plan corrective actions.
- Review and improve: Update documentation when risks, processes, technology, or business requirements change.
This approach helps keep the ISMS practical and relevant to the organization.
Choosing the Right Documentation Resources
The preparation of ISMS from the start may take considerable time and coordination. Editable documentation sources will come in handy, especially for companies requiring structured templates and examples.
The ISO 27001 documentation bundle provided by the website above contains an ISMS manual, 20 procedures, 29 policies, 9 SOPs, 49 sample templates, process flow diagrams, job descriptions, examples of risk assessment, statement of applicability, compliance matrix, and internal audit checklist consisting of over 500 questions.
This list may assist in structuring documentation and minimizing the effort required to create templates. However, each document should be checked and tailored according to the real scope, risks, and processes of an organization.
Conclusion
ISO 27001 documentation is useful for organizations when it comes to developing an organized way of doing things regarding information security, risk management, defining responsibilities, and maintaining accurate documentation. There are various documents, including the manual and the security policy, risk assessment, and audit checklists, which will be used in the development of different aspects of the ISMS. The Certification Consultancy offers ISO 27001 Documentation templates to assist in preparing your management system documents.
Promote your articles nowCheck for details
Choose a promotion package
Choose a package below, scan the QR code and pay the displayed amount for 20 days.
After payment, email your article title and payment screenshot to info@yourneeds.asia. Once confirmation is received, one of our administrators will activate the promotion.
Choose where your promoted article receives extra visibility
Promotion changes presentation and placement for the selected period. It does not guarantee traffic, enquiries, search ranking or sales.
Priority visibility in the VIP Lounge, promoted shelves and highlighted article areas.
Top-style highlighting in article directories, homepage feeds and promoted article blocks.
Premium styling across supported article feeds, recommendations and directory placements.
Featured presentation in supported homepage, category, directory and related-article areas.
Build a stronger online presence for your business
Get Your Website for ₹15,000
Are you listed and don't have a website for your business? We can plan, design and launch a responsive website that makes your business easier to understand and contact.
Get My WebsiteSEO Starts from ₹10,000/Month
Improve how your business is presented across Google, local listings and AI-powered search results with ongoing SEO, content and authority-building work.
Improve My VisibilitySuggested Articles
View all articles
Hydraulic Tractor Breaker: A Practical Attachment for Rock, Concrete and OFC Trenching Work
Hard rock, compact soil, asphalt and old concrete can slow down trenching, roadwork and utility installation projects. A hydraulic tractor breaker is a useful…
DPDP Act Compliance Checklist for Indian Startups
Picture this. It is 11 pm, your startup has just launched a new feature, and an investor asks, “Where exactly do we store user…
Top 10 Consent Management Platforms for DPDP Compliance
India's data privacy landscape is evolving rapidly with the Digital Personal Data Protection (DPDP) Act, 2023 and the DPDP Rules, 2025. As businesses collect…
Sod Sprigger Attachments: What Landscaping Teams Should Check Before Choosing
Landscaping projects can involve more than planting and finishing. When work includes sod or turf across a large area, teams also need to consider…
Latest Blog Posts
View all articles
Best Workday HCM Training in Pune at TechMyIndia: Discovering The Future of Digital HR
The new expectations from human resource technology Human resources have become intrinsically linked with digital business operations. Organizations require reliable methods of managing…
Explore service management workflows, operational problem-solving and enterprise platform knowledge with TechMyIndia in Hyderabad
IT Service Management begins with better problem solving If an business user loses access to a critical application, a team experiences system downtime, or…
Dholera News October 2026: Key Updates in One Place at Omana Projects
Dholera produces a steady stream of headlines, and not all of them are equally reliable or equally important. This roundup gathers the main updates…
Top Benefits of Hydrafacial Treatment in Delhi for Clear, Hydrated Skin
Top Benefits of Hydrafacial Treatment in Delhi for Clear, Hydrated Skin Healthy, glowing skin starts with the right skincare routine and professional care. If…
Top 10 Cookie Consent Management Platforms
Analytics, ad tools, third-party integrations: add any of them to a website and cookies follow. Keeping track of those cookies is now a basic…
From Student Demand to Institutional Strategy: Building a Clearer View of Education Market Potential
Education demand is often measured through enrolment. For an institution deciding whether to enter, expand or launch a new offering, enrolment is only the…