
Published: |Last updated:
Listen to this article
Show Quick ReadConcise summary from this article
Picture this. It is 11 pm, your startup has just launched a new feature, and an investor asks, “Where exactly do we store user phone numbers, and who can access them?” If the answer starts with a long pause, it may be time to review your data protection practices. India’s Digital Personal Data Protection Act, 2023 (DPDP Act) establishes a framework for handling digital personal data. With the Digital Personal…
Ask AI About This Article
Answers are limited to information in this article.
Picture this. It is 11 pm, your startup has just launched a new feature, and an investor asks, “Where exactly do we store user phone numbers, and who can access them?” If the answer starts with a long pause, it may be time to review your data protection practices.
India’s Digital Personal Data Protection Act, 2023 (DPDP Act) establishes a framework for handling digital personal data. With the Digital Personal Data Protection Rules, 2025 introducing a phased implementation timeline, startups should begin preparing their systems and processes now.
This practical checklist explains the key areas your business should review before the major compliance deadline in May 2027.
What the DPDP Act Means for Your Startup
The DPDP Act regulates the processing of digital personal data within its scope. This can include information such as names, email addresses, phone numbers, location details and payment-related information when it identifies an individual.
The law is not limited to large corporations. Startups and small businesses may also have obligations under the Act, depending on their activities and the law’s applicability.
Two important terms help explain the framework:
- Data Fiduciary: The person or organisation that determines the purpose and means of processing personal data.
- Data Principal: The individual to whom the personal data relates.
For example, if your startup operates an app that collects customer contact details to provide a service, your business may act as a Data Fiduciary, while the customers are Data Principals.
The DPDP Act Compliance Timeline
The DPDP Act, 2023, and the DPDP Rules, 2025 follow a phased implementation schedule. Different provisions become effective at different times, so businesses should not treat every obligation as having the same deadline.
| Milestone | Timeline |
| DPDP Rules, 2025 notified | November 2025 |
| Consent Manager-related provision under Section 6(9) | 13 November 2026 |
| Major remaining provisions under the phased schedule | 13 May 2027 |
The November 2026 date relates specifically to the Consent Manager provision under Section 6(9). It is not a universal deadline for every consent-related requirement.
The May 2027 date marks the 18-month implementation point for major provisions of the Act and Rules. Businesses should review the commencement schedule carefully to identify which requirements apply to their operations and when.
The transition period is an opportunity to prepare, rather than a reason to postpone compliance planning.
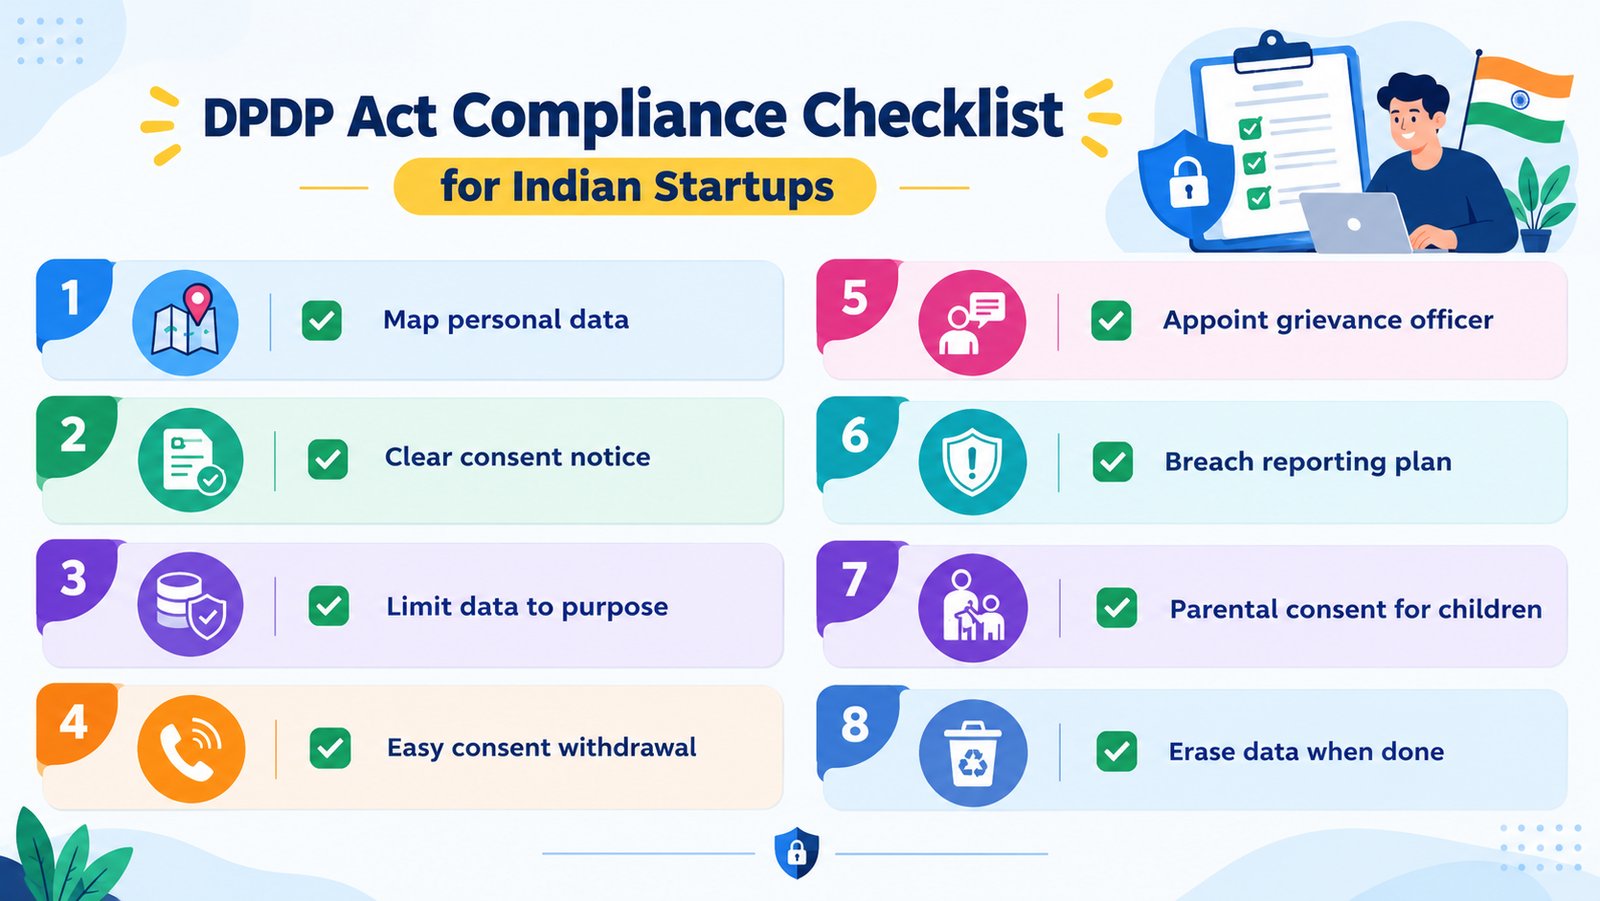
The Startup DPDP Compliance Checklist
Use these steps to begin reviewing your data protection practices. The exact requirements will depend on your business, the data you process and the applicable provisions.
Step 1: Map the personal data your business collects
Start by identifying where personal data enters your business and where it is stored.
Review your website forms, mobile apps, customer relationship management (CRM) systems, analytics tools, support emails, payment integrations and backups.
For each category of data, record:
- What information you collect.
- Why do you collect and use it?
- Where it is stored.
- Which employees, vendors or systems can access it.
- How long you need to retain it.
A simple spreadsheet is a useful starting point. Update it whenever you introduce a new feature or third-party tool.
Step 2: Review your privacy notices and consent process
The DPDP framework includes requirements for clear notices and valid consent where consent is the applicable legal basis for processing.
Avoid relying on a long, complicated privacy policy that users cannot easily understand. Explain what personal data you collect, the specific purpose of processing and how users can exercise their rights.
Your consent process should be designed to meet the applicable legal requirements. Make sure the notice is presented clearly and is connected to the actual data processing taking place.
Step 3: Make consent withdrawal straightforward
Where processing is based on consent, users must have a way to withdraw that consent. The Act requires withdrawal to be as easy as giving consent.
Review your app, website and account settings to see whether users can find the relevant option without unnecessary steps.
Also establish a process for handling withdrawal requests and assessing which processing activities must stop, subject to applicable legal requirements.
Step 4: Collect only the data you need
Review every field in your registration forms, checkout pages and customer surveys.
For example, if a food delivery service collects a user’s date of birth, it should have a clear reason for doing so. If the information is unnecessary for the service, consider removing the field.
Collecting less personal data can reduce security risks, simplify retention management and make your privacy practices easier to explain.
Step 5: Strengthen your security safeguards
The DPDP Act requires Data Fiduciaries to implement reasonable security safeguards to protect personal data.
Depending on your systems and risks, practical measures may include:
- Encryption where appropriate.
- Role-based access controls.
- Strong authentication for sensitive systems.
- Regular software updates and vulnerability reviews.
- Monitoring and security logging.
- Secure backups and recovery procedures.
Limit access to production data to people who need it for their work. Review access permissions periodically, particularly when employees change roles or leave the company.
Step 6: Prepare a personal data breach response plan
Your startup should know what to do if personal data is exposed, stolen or accessed without authorisation.
Create a written procedure that identifies who will investigate the incident, contain the problem, preserve relevant evidence and coordinate communications.
The applicable DPDP provisions include requirements concerning notification of personal data breaches to the Data Protection Board and affected individuals. Make sure your response process accounts for the relevant notification requirements and timelines once they apply.
Do not wait for an incident to decide who is responsible for responding.
Step 7: Establish data retention and deletion rules
Decide how long different categories of personal data need to be retained, taking applicable legal obligations into account.
For example, customer support records, inactive accounts, transaction information and security logs may have different retention needs.
The DPDP Rules, 2025 also contain requirements concerning the retention of certain logs and personal data. Some requirements apply according to the phased commencement schedule, so businesses should identify the relevant rules before finalising their retention policies.
Avoid keeping personal data indefinitely without a valid reason.
Step 8: Review how you handle children’s data
The DPDP Act defines a child as an individual who has not completed 18 years of age.
The framework includes specific obligations concerning the processing of children’s personal data, including verifiable parental consent, subject to applicable exemptions and rules.
If your product may be used by children, assess this early. Review your age-related workflows, parental consent process and the types of personal data your service collects.
A simple age confirmation checkbox should not automatically be treated as sufficient for every situation.
Step 9: Review vendors and cross-border data transfers
Your cloud hosting provider, payment gateway, email service and analytics tools may process personal data connected with your business.
Review the information you share with these providers, their security practices, contractual responsibilities and access permissions.
Also identify whether your business transfers personal data outside India. The DPDP Act permits cross-border transfers subject to applicable restrictions, including restrictions that the government may notify.
Do not assume that every international transfer is automatically prohibited or automatically permitted. Check the applicable requirements for your specific arrangement.
Step 10: Create a clear process for user requests
The DPDP Act provides Data Principals with rights that include access to information about personal data, correction and erasure, subject to the applicable provisions.
Publish a clear contact channel for privacy-related requests. Assign responsibility for receiving, verifying, tracking and responding to these requests.
Your internal procedure should also cover grievance handling and any applicable response timelines.
A dedicated email address can help, but an email address alone does not establish compliance. Your team needs a reliable process behind it.
Step 11: Train your team and document decisions
Data protection is not only a legal or technical responsibility. Product, marketing, sales, support and engineering teams may all handle personal data.
Provide practical training on collecting information, sharing data with vendors, managing access permissions and reporting suspected incidents.
Keep records of your data inventory, security reviews, vendor assessments, policy updates and decisions about retention. Good documentation helps your business understand its practices and demonstrate the steps it has taken.
DPDP Act Penalties: Why Startups Should Pay Attention
The DPDP Act provides for significant financial penalties for certain violations.
The maximum penalties under the Act’s Schedule include:
- Up to ₹250 crore for failure to take reasonable security safeguards to prevent personal data breaches.
- Up to ₹200 crore for specified violations involving children’s personal data.
- Up to ₹200 crore for failure to fulfil applicable obligations relating to notification of a personal data breach to the Board or affected individuals.
- Up to ₹50 crore for other violations covered by the relevant penalty entry.
These are statutory maximums, not automatic fines for every mistake. The applicable penalty depends on the nature of the contravention and the legal framework.
For a startup, the consequences of poor data protection can extend beyond regulatory penalties. A security incident may also damage customer trust, disrupt operations and affect relationships with business partners or investors.
Common DPDP Compliance Mistakes Startups Should Avoid
Several common mistakes can make compliance harder than necessary.
Assuming a privacy policy is enough: A published policy cannot compensate for consent processes, security measures or internal practices that do not meet applicable requirements.
Ignoring older customer data: Personal data collected years ago still needs appropriate handling. Review whether you need it and how it is protected.
Overlooking third-party tools: A business may share information with several vendors without maintaining a clear record of those arrangements.
Waiting until the deadline: Mapping data, changing systems and training employees can take time. Delaying these tasks may create avoidable pressure.
Copying another company’s policies: A template may be useful as a starting point, but your notices and procedures should reflect your own products and data processing activities.
FAQs:
- Does the DPDP Act apply to small startups?
The Act is not limited to large companies. It can apply to startups processing digital personal data within its scope. The specific obligations depend on the business and the relevant provisions.
- What is the main DPDP compliance deadline?
13 May 2027 is the 18-month implementation point for major provisions under the phased schedule. Certain provisions, including the Consent Manager-related provision under Section 6(9), have an earlier timeline of 13 November 2026.
- Is a privacy policy enough for DPDP compliance?
No. Depending on the applicable requirements, a business may also need appropriate notices and consent processes, security safeguards, breach-response procedures, retention practices and mechanisms for handling user requests.
- Do startups need to review their third-party vendors?
Yes. Reviewing vendors is a useful part of understanding where personal data goes, who can access it and what security and contractual arrangements are in place.
- Can a startup transfer personal data outside India?
Cross-border transfers are subject to the DPDP Act and any applicable government restrictions. Businesses should assess the specific transfer and the requirements in force rather than assume that all transfers are treated alike.
Your Next Step
Start with your data inventory this week. List the personal data your startup collects, the systems that store it and the people or vendors who can access it.
Once you understand your data flows, you can prioritise improvements to your notices, security safeguards, retention policies and user-request procedures.
DPDP compliance is not simply a task to complete before a deadline. It is an ongoing process of understanding how your business uses personal data and protecting that information responsibly.
Disclaimer: This article is for general informational purposes and is not legal advice. Businesses should review the applicable law, rules and commencement notifications and seek qualified advice where necessary.
Promote your articles nowCheck for details
Choose a promotion package
Choose a package below, scan the QR code and pay the displayed amount for 20 days.
After payment, email your article title and payment screenshot to info@yourneeds.asia. Once confirmation is received, one of our administrators will activate the promotion.
Choose where your promoted article receives extra visibility
Promotion changes presentation and placement for the selected period. It does not guarantee traffic, enquiries, search ranking or sales.
Priority visibility in the VIP Lounge, promoted shelves and highlighted article areas.
Top-style highlighting in article directories, homepage feeds and promoted article blocks.
Premium styling across supported article feeds, recommendations and directory placements.
Featured presentation in supported homepage, category, directory and related-article areas.
Build a stronger online presence for your business
Get Your Website for ₹15,000
Are you listed and don't have a website for your business? We can plan, design and launch a responsive website that makes your business easier to understand and contact.
Get My WebsiteSEO Starts from ₹10,000/Month
Improve how your business is presented across Google, local listings and AI-powered search results with ongoing SEO, content and authority-building work.
Improve My VisibilitySuggested Articles
View all articles
ISO 27001 Documents: A Complete Guide to Information Security Management
Introduction Information security is one of the critical components in the operation of any modern organization. Organizations utilize various computing devices, cloud services, networks,…
Hydraulic Tractor Breaker: A Practical Attachment for Rock, Concrete and OFC Trenching Work
Hard rock, compact soil, asphalt and old concrete can slow down trenching, roadwork and utility installation projects. A hydraulic tractor breaker is a useful…
Top 10 Consent Management Platforms for DPDP Compliance
India's data privacy landscape is evolving rapidly with the Digital Personal Data Protection (DPDP) Act, 2023 and the DPDP Rules, 2025. As businesses collect…
Sod Sprigger Attachments: What Landscaping Teams Should Check Before Choosing
Landscaping projects can involve more than planting and finishing. When work includes sod or turf across a large area, teams also need to consider…
Latest Blog Posts
View all articles
Dholera News October 2026: Key Updates in One Place at Omana Projects
Dholera produces a steady stream of headlines, and not all of them are equally reliable or equally important. This roundup gathers the main updates…
Top Benefits of Hydrafacial Treatment in Delhi for Clear, Hydrated Skin
Top Benefits of Hydrafacial Treatment in Delhi for Clear, Hydrated Skin Healthy, glowing skin starts with the right skincare routine and professional care. If…
Top 10 Cookie Consent Management Platforms
Analytics, ad tools, third-party integrations: add any of them to a website and cookies follow. Keeping track of those cookies is now a basic…
From Student Demand to Institutional Strategy: Building a Clearer View of Education Market Potential
Education demand is often measured through enrolment. For an institution deciding whether to enter, expand or launch a new offering, enrolment is only the…
حكم سداد الدين بعملة غير العملة الأصلية
قد يحتاج المدين في بعض الحالات إلى سداد ما عليه بعملة تختلف عن العملة التي ثبت بها الدين في الأصل، وهو ما يثير تساؤلًا…
La Grande Marquee Wedding Planner in Karachi: Décor, Stage, and Lighting Guide
An indoor marquee gives you something outdoor venues cannot: control. There is no wind to fight, no sudden rain, and no uneven light as…